mirror of
https://github.com/funkypenguin/geek-cookbook/
synced 2026-10-19 23:42:33 +00:00
Update for leanpub preview
This commit is contained in:
 AutoPenguin
@@ -104,7 +104,6 @@ networks:
|
||||
- subnet: 172.16.11.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
#### Assemble the tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's the conclusion to the [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
### Launch Autopirate stack
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
hero: AutoPirate - A fully-featured recipe to automate finding, downloading, and organising your media
|
||||
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [autopirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# Headphones
|
||||
@@ -46,7 +45,6 @@ headphones_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [autopirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# Heimdall
|
||||
@@ -52,7 +51,6 @@ To include Heimdall in your [AutoPirate](https://geek-cookbook.funkypenguin.co.n
|
||||
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [autopirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# Jackett
|
||||
@@ -46,7 +45,6 @@ jackett_proxy:
|
||||
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [autopirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# LazyLibrarian
|
||||
@@ -58,7 +57,6 @@ calibre-server:
|
||||
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
hero: AutoPirate - A fully-featured recipe to automate finding, downloading, and organising your media
|
||||
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [autopirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# Lidarr
|
||||
@@ -46,7 +45,6 @@ lidarr_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [autopirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# Mylar
|
||||
@@ -44,7 +43,6 @@ mylar_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# NZBGet
|
||||
@@ -14,7 +13,6 @@ NZBGet performs the same function as [SABnzbd](https://geek-cookbook.funkypengui
|
||||
To include NZBGet in your [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) stack
|
||||
(_The only reason you **wouldn't** use NZBGet, would be if you were using [SABnzbd](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/sabnzbd/) instead_), include the following in your autopirate.yml stack definition file:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
@@ -50,7 +48,6 @@ nzbget_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! note
|
||||
NZBGet uses a 401 header to prompt for authentication. When you use OAuth2_proxy, this seems to break. Since we trust OAuth to authenticate us, we can just disable NZGet's own authentication, by changing ControlPassword to null in nzbget.conf (i.e. ```ControlPassword=```)
|
||||
|
||||
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
|
||||
@@ -50,7 +49,6 @@ nzbhydra_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
|
||||
@@ -6,7 +5,6 @@
|
||||
|
||||
[NZBHydra 2](https://github.com/theotherp/nzbhydra2) is a meta search for NZB indexers. It provides easy access to a number of raw and newznab based indexers. You can search all your indexers from one place and use it as an indexer source for tools like Sonarr, Radarr or CouchPotato.
|
||||
|
||||
!!! note
|
||||
NZBHydra 2 is a complete rewrite of [NZBHydra (1)](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/nzbhybra/). It's currently in Beta. It works mostly fine but some functions might not be completely done and incompatibilities with some tools might still exist. You might want to run both in parallel for migration / testing purposes, but ultimately you'll probably want to switch over to NZBHydra 2 exclusively.
|
||||
|
||||

|
||||
@@ -65,7 +63,6 @@ nzbhydra2_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# Ombi
|
||||
@@ -51,7 +50,6 @@ ombi_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# Radarr
|
||||
@@ -22,7 +21,6 @@
|
||||
|
||||

|
||||
|
||||
!!! tip "Sponsored Project"
|
||||
Sonarr is one of my [sponsored projects](https://geek-cookbook.funkypenguin.co.nz/sponsored-projects/) - a project I financially support on a regular basis because of its utility to me. I forget it's there until I (reliably) receive an email with new and exciting updates
|
||||
|
||||
## Inclusion into AutoPirate
|
||||
@@ -62,7 +60,6 @@ radarr_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# RTorrent / ruTorrent
|
||||
@@ -50,7 +49,6 @@ rtorrent_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
# SABnzbd
|
||||
@@ -9,7 +8,6 @@ SABnzbd is the workhorse of the stack. It takes .nzb files as input (_manually o
|
||||
|
||||

|
||||
|
||||
!!! tip "Sponsored Project"
|
||||
SABnzbd is one of my [sponsored projects](https://geek-cookbook.funkypenguin.co.nz/sponsored-projects/) - a project I financially support on a regular basis because of its utility to me. It's not sexy, but it's consistent and reliable, and I enjoy the fruits of its labor near-daily.
|
||||
|
||||
## Inclusion into AutoPirate
|
||||
@@ -17,7 +15,6 @@ SABnzbd is the workhorse of the stack. It takes .nzb files as input (_manually o
|
||||
To include SABnzbd in your [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) stack
|
||||
(_The only reason you **wouldn't** use SABnzbd, would be if you were using [NZBGet](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/nzbget.md) instead_), include the following in your autopirate.yml stack definition file:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
@@ -53,7 +50,6 @@ sabnzbd_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! warning "Important Note re hostname validation"
|
||||
|
||||
(**Updated 10 June 2018**) : In SABnzbd [2.3.3](https://sabnzbd.org/wiki/extra/hostname-check.html), hostname verification was added as a mandatory check. SABnzbd will refuse inbound connections which weren't addressed to its own (_initially, autodetected_) hostname. This presents a problem within Docker Swarm, where container hostnames are random and disposable.
|
||||
|
||||
|
||||
@@ -1,4 +1,3 @@
|
||||
!!! warning
|
||||
This is not a complete recipe - it's a component of the [AutoPirate](https://geek-cookbook.funkypenguin.co.nz/recipes/autopirate/) "_uber-recipe_", but has been split into its own page to reduce complexity.
|
||||
|
||||
|
||||
@@ -8,7 +7,6 @@
|
||||
|
||||

|
||||
|
||||
!!! tip "Sponsored Project"
|
||||
Sonarr is one of my [sponsored projects](https://geek-cookbook.funkypenguin.co.nz/sponsored-projects/) - a project I financially support on a regular basis because of its utility to me. I forget it's there until I (reliably) receive an email with new and exciting updates
|
||||
|
||||
## Inclusion into AutoPirate
|
||||
@@ -48,7 +46,6 @@ sonarr_proxy:
|
||||
-authenticated-emails-file=/authenticated-emails.txt
|
||||
```
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
## Assemble more tools..
|
||||
|
||||
@@ -22,7 +22,6 @@ Bitwarden is a free and open source password management solution for individuals
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! summary "Ingredients"
|
||||
Existing:
|
||||
|
||||
1. [X] [Docker swarm cluster](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/design/) with [persistent shared storage](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/shared-storage-ceph.md)
|
||||
@@ -42,14 +41,12 @@ mkdir /var/data/bitwarden
|
||||
|
||||
Create `/var/data/config/bitwarden/bitwarden.env`, and **leave it empty for now**.
|
||||
|
||||
!!! question
|
||||
What, why an empty env file? Well, the container supports lots of customizations via environment variables, for things like toggling self-registration, 2FA, etc. These are too complex to go into for this recipe, but readers are recommended to review the [dani-garcia/bitwarden_rs wiki](https://github.com/dani-garcia/bitwarden_rs), and customize their installation to suite.
|
||||
|
||||
### Setup Docker Swarm
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -78,7 +75,6 @@ networks:
|
||||
external: true
|
||||
```
|
||||
|
||||
!!! note
|
||||
Note the clever use of two Traefik frontends to expose the notifications hub on port 3012. Thanks @gkoerk!
|
||||
|
||||
|
||||
|
||||
@@ -52,7 +52,6 @@ DB_PASSWORD=secret
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -126,7 +125,6 @@ networks:
|
||||
- subnet: 172.16.33.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -59,7 +59,6 @@ Follow the [instructions](https://github.com/bitly/oauth2_proxy) to setup your o
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -109,7 +108,6 @@ networks:
|
||||
- subnet: 172.16.18.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
# Collabora Online
|
||||
|
||||
!!! important
|
||||
Development of this recipe is sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
@@ -52,7 +51,6 @@ mkdir /var/data/config/collabora/
|
||||
|
||||
Create /var/data/config/collabora/collabora.env, and populate with the following variables, customized for your installation.
|
||||
|
||||
!!! warning
|
||||
Note the following:
|
||||
|
||||
1. Variables are in lower-case, unlike our standard convention. This is to align with the CODE container
|
||||
@@ -156,7 +154,6 @@ Create an empty ```/var/data/collabora/loolwsd.xml``` by running ```touch /var/d
|
||||
|
||||
Create ```/var/data/config/collabora/collabora.yml``` as follows, changing the traefik frontend_rule as necessary:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
@@ -295,7 +292,6 @@ In NextCloud, Install the **Collabora Online** app (https://apps.nextcloud.com/a
|
||||
|
||||
Now browse your NextCloud files. Click the plus (+) sign to create a new document, and create either a new document, spreadsheet, or presentation. Name your document and then click on it. If Collabora is setup correctly, you'll shortly enter into the rich editing interface provided by Collabora :)
|
||||
|
||||
!!! important
|
||||
Development of this recipe is sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
|
||||
@@ -67,7 +67,6 @@ OPTIONS=--allow-source-mismatch --exclude /var/data/runtime --exclude /var/data/
|
||||
PASSPHRASE=<YOUR CHOSEN PASSPHRASE>
|
||||
```
|
||||
|
||||
!!! note
|
||||
See the [data layout reference](https://geek-cookbook.funkypenguin.co.nz/reference/data_layout/) for an explanation of the included/excluded paths above.
|
||||
|
||||
### Run a test backup
|
||||
@@ -87,7 +86,6 @@ You should see some activity, with a summary of bytes transferred at the end.
|
||||
|
||||
Repeat after me: "If you don't verify your backup, **it's not a backup**".
|
||||
|
||||
!!! warning
|
||||
Depending on what tier of storage you chose from your provider (_i.e., Google Coldline, or Amazon S3_), you may be charged for downloading data.
|
||||
|
||||
Run a variation of the following to confirm a file you expect to be backed up, **is** backed up. (_I used traefik.yml from the [traefik recipie](https://geek-cookbook.funkypenguin.co.nz/recipie/traefik/), since this is likely to exist for every reader_).
|
||||
@@ -119,7 +117,6 @@ Examine the contents of /var/data/duplicity/tmp/traefik-restored.yml to confirm
|
||||
|
||||
Now that we have confidence in our backup/restore process, let's automate it by creating a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -147,7 +144,6 @@ networks:
|
||||
- subnet: 172.16.10.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -6,7 +6,6 @@ Don't be like [Cameron](http://haltandcatchfire.wikia.com/wiki/Cameron_Howe). Ba
|
||||
|
||||
<iframe width="560" height="315" src="https://www.youtube.com/embed/1UtFeMoqVHQ" frameborder="0" allow="accelerometer; autoplay; encrypted-media; gyroscope; picture-in-picture" allowfullscreen></iframe>
|
||||
|
||||
!!! important
|
||||
Ongoing development of this recipe is sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
@@ -60,7 +59,6 @@ OAUTH2_PROXY_COOKIE_SECRET=
|
||||
|
||||
Create ```/var/data/config/elkarbackup/elkarbackup-db-backup.env```, and populate with the following, to setup the nightly database dump.
|
||||
|
||||
!!! note
|
||||
Running a daily database dump might be considered overkill, since ElkarBackup can be configured to backup its own database. However, making my own backup keeps the operation of this stack consistent with **other** stacks which employ MariaDB.
|
||||
|
||||
Also, did you ever hear about the guy who said "_I wish I had fewer backups"?
|
||||
@@ -79,7 +77,6 @@ BACKUP_FREQUENCY=1d
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -158,7 +155,6 @@ networks:
|
||||
- subnet: 172.16.36.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
@@ -222,14 +218,12 @@ echo "Available disk space: $AVAILABLE"
|
||||
echo ""
|
||||
```
|
||||
|
||||
!!! note
|
||||
You'll note that I don't use the script to create a mysql dump (_since Elkar is running within a container anyway_), rather I just rely on the database dump which is made nightly into ```/var/data/elkarbackup/database-dump/```
|
||||
|
||||
### Restoring data
|
||||
|
||||
Repeat after me : "**It's not a backup unless you've tested a restore**"
|
||||
|
||||
!!! note
|
||||
I had some difficulty making restoring work well in the webUI. My attempts to "Restore to client" failed with an SSH error about "localhost" not found. I **was** able to download the backup from my web browser, so I considered it a successful restore, since I can retrieve the backed-up data either from the webUI or from the filesystem directly.
|
||||
|
||||
To restore files form a job, click on the "Restore" button in the WebUI, while on the **Jobs** tab:
|
||||
@@ -238,7 +232,6 @@ To restore files form a job, click on the "Restore" button in the WebUI, while o
|
||||
|
||||
This takes you to a list of backup names and file paths. You can choose to download the entire contents of the backup from your browser as a .tar.gz, or to restore the backup to the client. If you click on the **name** of the backup, you can also drill down into the file structure, choosing to restore a single file or directory.
|
||||
|
||||
!!! important
|
||||
Ongoing development of this recipe is sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
|
||||
@@ -35,7 +35,6 @@ GUID=
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -70,7 +69,6 @@ networks:
|
||||
- subnet: 172.16.17.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -8,7 +8,6 @@ hero: Ghost - A recipe for beautiful online publication.
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! summary "Ingredients"
|
||||
Existing:
|
||||
|
||||
1. [X] [Docker swarm cluster](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/design/) with [persistent shared storage](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/shared-storage-ceph.md)
|
||||
@@ -30,7 +29,6 @@ mkdir -p /var/data/ghost
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
|
||||
@@ -6,7 +6,6 @@ While a runner isn't strictly required to use GitLab, if you want to do CI, you'
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! summary "Ingredients"
|
||||
Existing:
|
||||
|
||||
1. [X] [Docker swarm cluster](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/design/) with [persistent shared storage](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/shared-storage-ceph.md)
|
||||
@@ -31,7 +30,6 @@ mkdir -p {runners/1,runners/2}
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
|
||||
@@ -8,7 +8,6 @@ Docker does maintain an [official "Omnibus" container](https://docs.gitlab.com/o
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! summary "Ingredients"
|
||||
Existing:
|
||||
|
||||
1. [X] [Docker swarm cluster](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/design/) with [persistent shared storage](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/shared-storage-ceph.md)
|
||||
@@ -61,7 +60,6 @@ GITLAB_ROOT_PASSWORD=changeme
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
@@ -115,7 +113,6 @@ networks:
|
||||
- subnet: 172.16.2.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -27,13 +27,11 @@ As you'll note in the (_real world_) screenshot above, my requirements for a per
|
||||
|
||||
Gollum meets all these requirements, and as an added bonus, is extremely fast and lightweight.
|
||||
|
||||
!!! note
|
||||
Since Gollum itself offers no user authentication, this design secures gollum behind an [oauth2 proxy](https://geek-cookbook.funkypenguin.co.nz/reference/oauth_proxy/), so that in order to gain access to the Gollum UI at all, oauth2 authentication (_to GitHub, GitLab, Google, etc_) must have already occurred.
|
||||
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! summary "Ingredients"
|
||||
Existing:
|
||||
|
||||
1. [X] [Docker swarm cluster](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/design/) with [persistent shared storage](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/shared-storage-ceph.md)
|
||||
@@ -67,7 +65,6 @@ OAUTH2_PROXY_COOKIE_SECRET=
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
```
|
||||
version: '3'
|
||||
@@ -116,7 +113,6 @@ networks:
|
||||
- subnet: 172.16.9.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -42,7 +42,6 @@ GF_AUTH_BASIC_ENABLED=false
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -117,7 +116,6 @@ networks:
|
||||
- subnet: 172.16.13.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
## Serving
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
# iBeacons with Home assistant
|
||||
|
||||
!!! warning
|
||||
This is not a complete recipe - it's an optional additional of the [HomeAssistant](https://geek-cookbook.funkypenguin.co.nz/recipes/homeassistant/) "recipe", since it only applies to a subset of users
|
||||
|
||||
One of the most useful features of Home Assistant is location awareness. I don't care if someone opens my office door when I'm home, but you bet I care about (_and want to be notified_) it if I'm away!
|
||||
|
||||
@@ -68,7 +68,6 @@ BACKUP_FREQUENCY=1d
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -129,7 +128,6 @@ networks:
|
||||
- subnet: 172.16.6.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -10,7 +10,6 @@ Great power, right? A client (_yes, you can [hire](https://www.funkypenguin.co.n
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! summary "Ingredients"
|
||||
Existing:
|
||||
|
||||
1. [X] [Docker swarm cluster](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/design/) with [persistent shared storage](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/shared-storage-ceph.md)
|
||||
@@ -32,7 +31,6 @@ mkdir -p /var/data/instapy/logs
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -67,7 +65,6 @@ services:
|
||||
- "5900:5900"
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
### Command your bot
|
||||
|
||||
@@ -1,8 +1,6 @@
|
||||
!!! danger "This recipe is a work in progress"
|
||||
This recipe is **incomplete**, and remains a work in progress.
|
||||
So... There may be errors and inaccuracies. Jump into [Discord](http://chat.funkypenguin.co.nz) if you're encountering issues
|
||||
|
||||
!!! important
|
||||
Development of this recipe is sponsored by [The Common Observatory](https://www.observe.global/)
|
||||
|
||||
# IPFS
|
||||
@@ -134,7 +132,6 @@ You'll see output like this:
|
||||
10:55:26.625 INFO cluster: ** IPFS Cluster is READY ** cluster.go:418
|
||||
```
|
||||
|
||||
!!! note
|
||||
You can ignore the warnings about port 5001 refused - this is because we weren't running the ipfs daemon while bootstrapping the cluster. Its harmless.
|
||||
|
||||
I haven't worked out why yet, but running the bootstrap in docker-run format reset the permissions on /var/ipfs/cluster/, so look at /var/ipfs/daemon, and make the permissions of /var/ipfs/cluster the same.
|
||||
|
||||
@@ -4,7 +4,6 @@ hero: Kanboard - A recipe to get your personal kanban on
|
||||
|
||||
Kanboard is a Kanban tool, developed by [Frdric Guillot](https://github.com/fguillot). (_Who also happens to be the developer of my favorite RSS reader, [Miniflux](https://geek-cookbook.funkypenguin.co.nz/recipes/miniflux/)_)
|
||||
|
||||
!!! tip "Sponsored Project"
|
||||
Kanboard is one of my [sponsored projects](https://geek-cookbook.funkypenguin.co.nz/sponsored-projects/) - a project I financially support on a regular basis because of its utility to me. I use it both in my DayJob(tm), and to manage my overflowing, overly-optimistic personal commitments!
|
||||
|
||||
Features include:
|
||||
@@ -54,7 +53,6 @@ OAUTH2_PROXY_COOKIE_SECRET=
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
|
||||
@@ -2,7 +2,6 @@
|
||||
|
||||
[KeyCloak](https://www.keycloak.org/) is "*an open source identity and access management solution*". Using a local database, or a variety of backends (_think [OpenLDAP](https://geek-cookbook.funkypenguin.co.nz/recipes/openldap/)_), you can provide Single Sign-On (SSO) using OpenID, OAuth 2.0, and SAML. KeyCloak's OpenID provider can be used in combination with [Traefik Forward Auth](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/traefik-forward-auth/), to protect [vulnerable services](https://geek-cookbook.funkypenguin.co.nz/recipe/nzbget/) with an extra layer of authentication.
|
||||
|
||||
!!! important
|
||||
Initial development of this recipe was sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
@@ -11,7 +10,6 @@
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! Summary
|
||||
Existing:
|
||||
|
||||
* [X] [Docker swarm cluster](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/design/) with [persistent shared storage](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/shared-storage-ceph/)
|
||||
@@ -68,7 +66,6 @@ BACKUP_FREQUENCY=1d
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
```
|
||||
version: '3'
|
||||
@@ -126,7 +123,6 @@ networks:
|
||||
- subnet: 172.16.49.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
@@ -138,7 +134,6 @@ Launch the KeyCloak stack by running ```docker stack deploy keycloak -c <path -t
|
||||
|
||||
Log into your new instance at https://**YOUR-FQDN**, and login with the user/password you defined in `keycloak.env`.
|
||||
|
||||
!!! important
|
||||
Initial development of this recipe was sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
|
||||
@@ -1,13 +1,11 @@
|
||||
# Authenticate KeyCloak against OpenLDAP
|
||||
|
||||
!!! warning
|
||||
This is not a complete recipe - it's an **optional** component of the [Keycloak recipe](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/), but has been split into its own page to reduce complexity.
|
||||
|
||||
KeyCloak gets really sexy when you integrate it into your [OpenLDAP](https://geek-cookbook.funkypenguin.co.nz/recipes/openldap/) stack (_also, it's great not to have to play with ugly LDAP tree UIs_). Note that OpenLDAP integration is **not necessary** if you want to use KeyCloak with [Traefik Forward Auth](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/traefik-forward-auth/) - all you need for that is [local users](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/create-user/), and an [OIDC client](http://localhost:8000/recipes/keycloak/setup-oidc-provider/).
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! Summary
|
||||
Existing:
|
||||
|
||||
* [X] [KeyCloak](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/) recipe deployed successfully
|
||||
@@ -60,7 +58,6 @@ For each of the following mappers, click the name, and set the "_Read Only_" fla
|
||||
|
||||
We've setup a new realm in KeyCloak, and configured read-write federation to an [OpenLDAP](https://geek-cookbook.funkypenguin.co.nz/recipes/openldap/) backend. We can now manage our LDAP users using either KeyCloak or LDAP directly, and we can protect vulnerable services using [Traefik Forward Auth](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/traefik-forward-auth/).
|
||||
|
||||
!!! Summary
|
||||
Created:
|
||||
|
||||
* [X] KeyCloak realm in read-write federation with [OpenLDAP](https://geek-cookbook.funkypenguin.co.nz/recipes/openldap/) directory
|
||||
|
||||
@@ -1,13 +1,11 @@
|
||||
# Create KeyCloak Users
|
||||
|
||||
!!! warning
|
||||
This is not a complete recipe - it's an optional component of the [Keycloak recipe](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/), but has been split into its own page to reduce complexity.
|
||||
|
||||
Unless you plan to authenticate against an outside provider (*[OpenLDAP](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/openldap/), below, for example*), you'll want to create some local users..
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! Summary
|
||||
Existing:
|
||||
|
||||
* [X] [KeyCloak](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/) recipe deployed successfully
|
||||
@@ -32,7 +30,6 @@ Once your user is created, to set their password, click on the "**Credentials**"
|
||||
|
||||
We've setup users in KeyCloak, which we can now use to authenticate to KeyCloak, when it's used as an [OIDC Provider](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/setup-oidc-provider/), potentially to secure vulnerable services using [Traefik Forward Auth](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/traefik-forward-auth/).
|
||||
|
||||
!!! Summary
|
||||
Created:
|
||||
|
||||
* [X] Username / password to authenticate against [KeyCloak](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/)
|
||||
|
||||
@@ -1,13 +1,11 @@
|
||||
# Add OIDC Provider to KeyCloak
|
||||
|
||||
!!! warning
|
||||
This is not a complete recipe - it's an optional component of the [Keycloak recipe](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/), but has been split into its own page to reduce complexity.
|
||||
|
||||
Having an authentication provider is not much use until you start authenticating things against it! In order to authenticate against KeyCloak using OpenID Connect (OIDC), which is required for [Traefik Forward Auth](https://geek-cookbook.funkypenguin.co.nz/recipe/traefik-forward-auth/), we'll setup a client in KeyCloak...
|
||||
|
||||
## Ingredients
|
||||
|
||||
!!! Summary
|
||||
Existing:
|
||||
|
||||
* [X] [KeyCloak](https://geek-cookbook.funkypenguin.co.nz/recipes/keycloak/) recipe deployed successfully
|
||||
@@ -47,7 +45,6 @@ Now that you've changed the access type, and clicked **Save**, an additional **C
|
||||
|
||||
We've setup an OIDC client in KeyCloak, which we can now use to protect vulnerable services using [Traefik Forward Auth](https://geek-cookbook.funkypenguin.co.nz/ha-docker-swarm/traefik-forward-auth/). The OIDC URL provided by KeyCloak in the master realm, is *https://<your-keycloak-url\>/realms/master/.well-known/openid-configuration*
|
||||
|
||||
!!! Summary
|
||||
Created:
|
||||
|
||||
* [X] Client ID and Client Secret used to authenticate against KeyCloak with OpenID Connect
|
||||
|
||||
@@ -4,7 +4,6 @@ Kanboard is a Kanban tool, developed by [Frdric Guillot](https://github.com/fgui
|
||||
|
||||
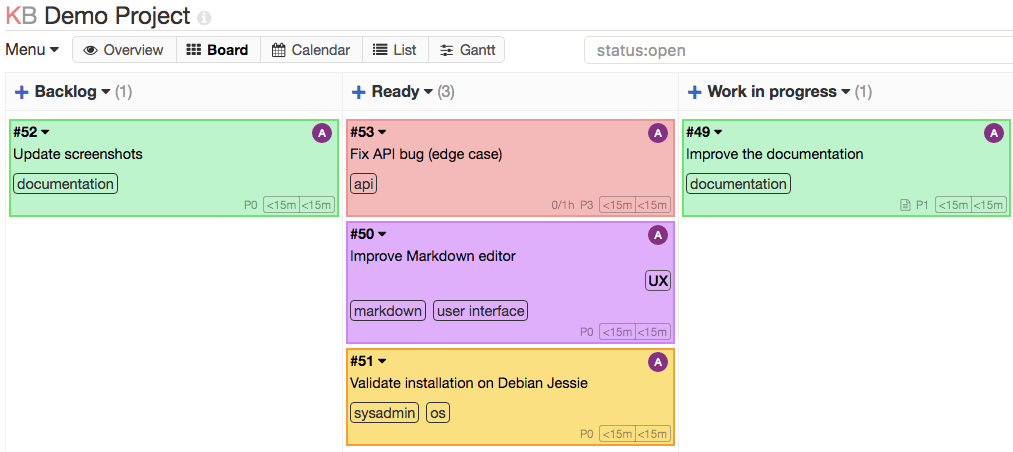
|
||||
|
||||
!!! tip "Sponsored Project"
|
||||
Kanboard is one of my [sponsored projects](https://geek-cookbook.funkypenguin.co.nz/sponsored-projects/) - a project I financially support on a regular basis because of its utility to me. I use it both in my DayJob(tm), and to manage my overflowing, overly-optimistic personal commitments!
|
||||
|
||||
Features include:
|
||||
@@ -89,7 +88,6 @@ EOF
|
||||
kubectl create -f /var/data/config/kanboard/kanboard-volumeclaim.yaml
|
||||
```
|
||||
|
||||
!!! question "What's that annotation about?"
|
||||
The annotation is used by [k8s-snapshots](https://geek-cookbook.funkypenguin.co.nz/kubernetes/snapshots/) to create daily incremental snapshots of your persistent volumes. In this case, our volume is snapshotted daily, and copies kept for 7 days.
|
||||
|
||||
### Create ConfigMap
|
||||
@@ -116,7 +114,6 @@ Now that we have a [namespace](https://kubernetes.io/docs/concepts/overview/work
|
||||
|
||||
Create a deployment to tell Kubernetes about the desired state of the pod (*which it will then attempt to maintain*). Note below that we mount the persistent volume **twice**, to both ```/var/www/app/data``` and ```/var/www/app/plugins```, using the subPath value to differentiate them. This trick avoids us having to provision **two** persistent volumes just for data mounted in 2 separate locations.
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary .yml files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```kubectl create -f *.yml```
|
||||
|
||||
```
|
||||
|
||||
@@ -4,7 +4,6 @@ Miniflux is a lightweight RSS reader, developed by [Frdric Guillot](https://gith
|
||||
|
||||
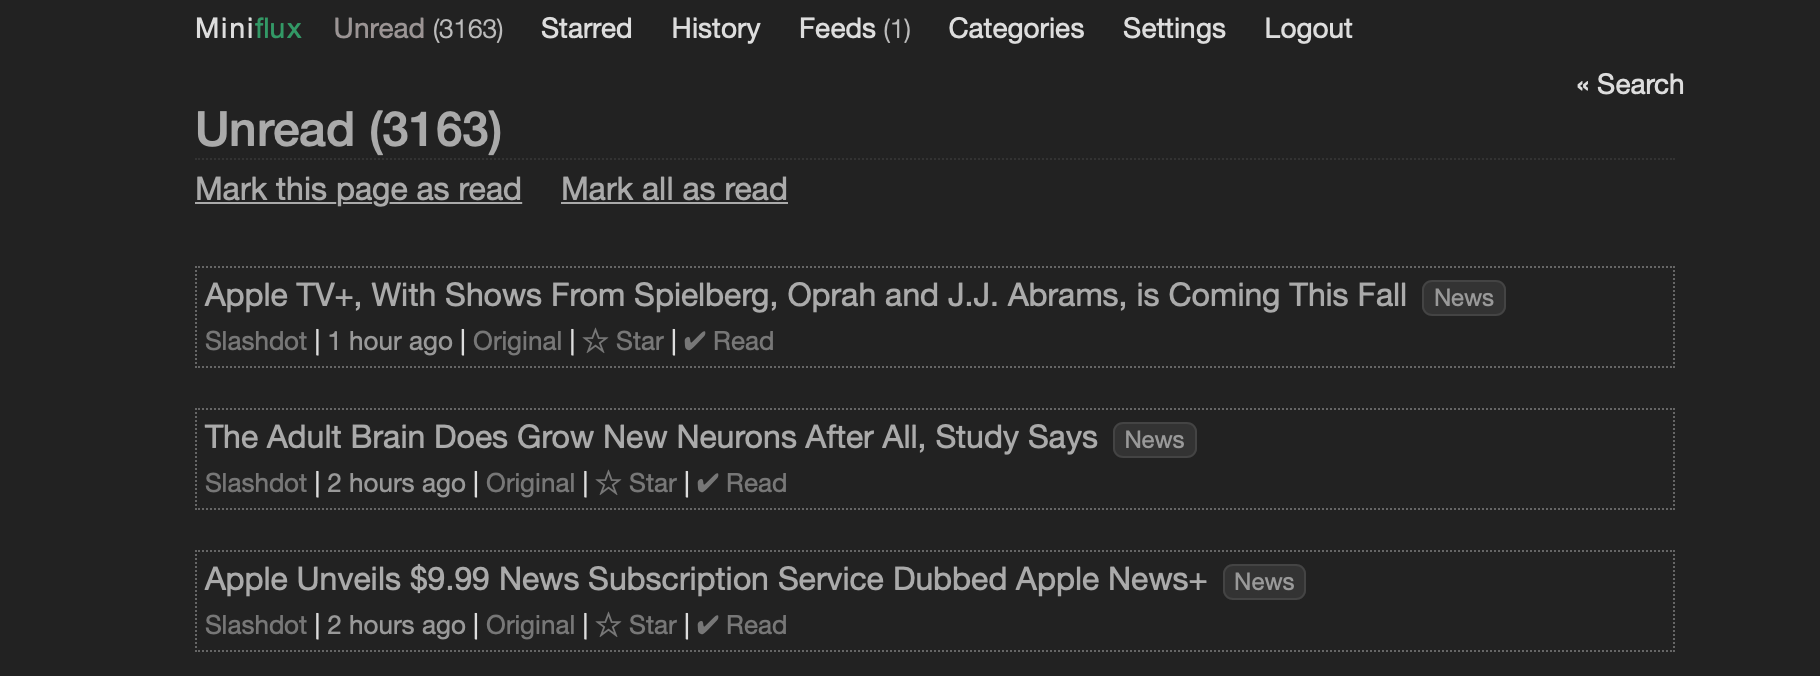
|
||||
|
||||
!!! tip "Sponsored Project"
|
||||
Miniflux is one of my [sponsored projects](https://geek-cookbook.funkypenguin.co.nz/sponsored-projects/) - a project I financially support on a regular basis because of its utility to me. Although I get to process my RSS feeds less frequently than I'd like to!
|
||||
|
||||
I've [reviewed Miniflux in detail on my blog](https://www.funkypenguin.co.nz/review/miniflux-lightweight-self-hosted-rss-reader/), but features (among many) that I appreciate:
|
||||
@@ -14,7 +13,6 @@ I've [reviewed Miniflux in detail on my blog](https://www.funkypenguin.co.nz/rev
|
||||
* Feeds can be configured to download a "full" version of the content (_rather than an excerpt_)
|
||||
* Use the Bookmarklet to subscribe to a website directly from any browsers
|
||||
|
||||
!!! abstract "2.0+ is a bit different"
|
||||
[Some things changed](https://docs.miniflux.net/en/latest/migration.html) when Miniflux 2.0 was released. For one thing, the only supported database is now postgresql (_no more SQLite_). External themes are gone, as is PHP (_in favor of golang_). It's been a controversial change, but I'm keen on minimal and single-purpose, so I'm still very happy with the direction of development. The developer has laid out his [opinions](https://docs.miniflux.net/en/latest/opinionated.html) re the decisions he's made in the course of development.
|
||||
|
||||
|
||||
@@ -87,7 +85,6 @@ EOF
|
||||
kubectl create -f /var/data/config/miniflux/db-persistent-volumeclaim.yaml
|
||||
```
|
||||
|
||||
!!! question "What's that annotation about?"
|
||||
The annotation is used by [k8s-snapshots](https://geek-cookbook.funkypenguin.co.nz/kubernetes/snapshots/) to create daily incremental snapshots of your persistent volumes. In this case, our volume is snapshotted daily, and copies kept for 7 days.
|
||||
|
||||
### Create secrets
|
||||
@@ -105,7 +102,6 @@ kubectl create secret -n mqtt generic miniflux-credentials \
|
||||
--from-file=database-url.secret
|
||||
```
|
||||
|
||||
!!! tip "Why use ```echo -n```?"
|
||||
Because. See [my blog post here](https://www.funkypenguin.co.nz/beware-the-hidden-newlines-in-kubernetes-secrets/) for the pain of hunting invisible newlines, that's why!
|
||||
|
||||
|
||||
@@ -117,7 +113,6 @@ Now that we have a [namespace](https://kubernetes.io/docs/concepts/overview/work
|
||||
|
||||
Deployments tell Kubernetes about the desired state of the pod (*which it will then attempt to maintain*). Create the db deployment by excecuting the following. Note that the deployment refers to the secrets created above.
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary .yml files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```kubectl create -f *.yml```
|
||||
|
||||
```
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
hero: Not all heroes wear capes
|
||||
|
||||
!!! danger "This recipe is a work in progress"
|
||||
This recipe is **incomplete**, and is featured to align the [patrons](https://www.patreon.com/funkypenguin)'s "premix" repository with the cookbook. "_premix_" is a private git repository available to [all Patreon patrons](https://www.patreon.com/funkypenguin), which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
So... There may be errors and inaccuracies. Jump into [Discord](http://chat.funkypenguin.co.nz) if you're encountering issues
|
||||
@@ -56,7 +55,6 @@ MAIL_FROM="Wekan <wekan@wekan.example.com>"
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -109,7 +107,6 @@ networks:
|
||||
- subnet: 172.16.3.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -49,7 +49,6 @@ MAIL_FROM="Wekan <wekan@wekan.example.com>"
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -102,7 +101,6 @@ networks:
|
||||
- subnet: 172.16.3.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
hero: Not all heroes wear capes
|
||||
|
||||
!!! danger "This recipe is a work in progress"
|
||||
This recipe is **incomplete**, and is featured to align the [patrons](https://www.patreon.com/funkypenguin)'s "premix" repository with the cookbook. "_premix_" is a private git repository available to [all Patreon patrons](https://www.patreon.com/funkypenguin), which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
So... There may be errors and inaccuracies. Jump into [Discord](http://chat.funkypenguin.co.nz) if you're encountering issues
|
||||
@@ -56,7 +55,6 @@ MAIL_FROM="Wekan <wekan@wekan.example.com>"
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -109,7 +107,6 @@ networks:
|
||||
- subnet: 172.16.3.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -4,7 +4,6 @@ Kanboard is a Kanban tool, developed by [Frdric Guillot](https://github.com/fgui
|
||||
|
||||

|
||||
|
||||
!!! tip "Sponsored Project"
|
||||
Kanboard is one of my [sponsored projects](https://geek-cookbook.funkypenguin.co.nz/sponsored-projects/) - a project I financially support on a regular basis because of its utility to me. I use it both in my DayJob(tm), and to manage my overflowing, overly-optimistic personal commitments!
|
||||
|
||||
Features include:
|
||||
@@ -89,7 +88,6 @@ EOF
|
||||
kubectl create -f /var/data/config/kanboard/kanboard-volumeclaim.yaml
|
||||
```
|
||||
|
||||
!!! question "What's that annotation about?"
|
||||
The annotation is used by [k8s-snapshots](https://geek-cookbook.funkypenguin.co.nz/kubernetes/snapshots/) to create daily incremental snapshots of your persistent volumes. In this case, our volume is snapshotted daily, and copies kept for 7 days.
|
||||
|
||||
### Create ConfigMap
|
||||
@@ -116,7 +114,6 @@ Now that we have a [namespace](https://kubernetes.io/docs/concepts/overview/work
|
||||
|
||||
Create a deployment to tell Kubernetes about the desired state of the pod (*which it will then attempt to maintain*). Note below that we mount the persistent volume **twice**, to both ```/var/www/app/data``` and ```/var/www/app/plugins```, using the subPath value to differentiate them. This trick avoids us having to provision **two** persistent volumes just for data mounted in 2 separate locations.
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary .yml files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```kubectl create -f *.yml```
|
||||
|
||||
```
|
||||
|
||||
@@ -94,7 +94,6 @@ Create the necessary DNS TXT entries for your domain(s). Note that although open
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (_v3.2 - because we need to expose mail ports in "host mode"_), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
@@ -154,7 +153,6 @@ networks:
|
||||
- subnet: 172.16.2.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot.
|
||||
|
||||
A sample docker-mailserver.env file looks like this:
|
||||
|
||||
@@ -48,7 +48,6 @@ BACKUP_FREQUENCY=1d
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -103,7 +102,6 @@ networks:
|
||||
- subnet: 172.16.40.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -6,7 +6,6 @@ Miniflux is a lightweight RSS reader, developed by [Frdric Guillot](https://gith
|
||||
|
||||

|
||||
|
||||
!!! tip "Sponsored Project"
|
||||
Miniflux is one of my [sponsored projects](https://geek-cookbook.funkypenguin.co.nz/sponsored-projects/) - a project I financially support on a regular basis because of its utility to me. Although I get to process my RSS feeds less frequently than I'd like to!
|
||||
|
||||
I've [reviewed Miniflux in detail on my blog](https://www.funkypenguin.co.nz/review/miniflux-lightweight-self-hosted-rss-reader/), but features (among many) that I appreciate:
|
||||
@@ -16,7 +15,6 @@ I've [reviewed Miniflux in detail on my blog](https://www.funkypenguin.co.nz/rev
|
||||
* Feeds can be configured to download a "full" version of the content (_rather than an excerpt_)
|
||||
* Use the Bookmarklet to subscribe to a website directly from any browsers
|
||||
|
||||
!!! abstract "2.0+ is a bit different"
|
||||
[Some things changed](https://docs.miniflux.net/en/latest/migration.html) when Miniflux 2.0 was released. For one thing, the only supported database is now postgresql (_no more SQLite_). External themes are gone, as is PHP (_in favor of golang_). It's been a controversial change, but I'm keen on minimal and single-purpose, so I'm still very happy with the direction of development. The developer has laid out his [opinions](https://docs.miniflux.net/en/latest/opinionated.html) re the decisions he's made in the course of development.
|
||||
|
||||
## Ingredients
|
||||
@@ -68,7 +66,6 @@ The entire application is configured using environment variables, including the
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
|
||||
@@ -45,7 +45,6 @@ MINIO_SECRET_KEY=<another random, complex string>
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
hero: Kubernetes. The hero we deserve.
|
||||
|
||||
!!! danger "This recipe is a work in progress"
|
||||
This recipe is **incomplete**, and is featured to align the [patrons](https://www.patreon.com/funkypenguin)'s "premix" repository with the cookbook. "_premix_" is a private git repository available to [all Patreon patrons](https://www.patreon.com/funkypenguin), which includes all the necessary .yml files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```kubectl create -f *.yml```
|
||||
|
||||
So... There may be errors and inaccuracies. Jump into [Discord](http://chat.funkypenguin.co.nz) if you're encountering issues
|
||||
@@ -104,7 +103,6 @@ kubectl create secret -n mqtt generic mqtt-credentials \
|
||||
--from-file=letsencrypt-email.secret
|
||||
```
|
||||
|
||||
!!! tip "Why use ```echo -n```?"
|
||||
Because. See [my blog post here](https://www.funkypenguin.co.nz/beware-the-hidden-newlines-in-kubernetes-secrets/) for the pain of hunting invisible newlines, that's why!
|
||||
|
||||
## Serving
|
||||
@@ -113,7 +111,6 @@ kubectl create secret -n mqtt generic mqtt-credentials \
|
||||
|
||||
Now that we have a volume, a service, and a namespace, we can create a deployment for the mqtt pod. Note below the use of volume mounts, environment variables, as well as the secrets.
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary .yml files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```kubectl create -f *.yml```
|
||||
|
||||
```
|
||||
|
||||
@@ -73,7 +73,6 @@ SNMP_NODES="router1:10.0.0.254:9999"
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -122,7 +121,6 @@ networks:
|
||||
- subnet: 172.16.24.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -2,7 +2,6 @@ hero: Backup all your stuff. Share it. Privately.
|
||||
|
||||
# NextCloud
|
||||
|
||||
!!! important
|
||||
Ongoing development of this recipe is sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
@@ -70,7 +69,6 @@ BACKUP_FREQUENCY=1d
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -158,7 +156,6 @@ networks:
|
||||
- subnet: 172.16.12.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
@@ -224,7 +221,6 @@ location: https://nextcloud.batcave.org/remote.php/dav/
|
||||
|
||||
Note that this .htaccess can be overwritten by NextCloud, and you may have to reapply the change in future. I've created an [issue requesting a permanent fix](https://github.com/nextcloud/docker/issues/577).
|
||||
|
||||
!!! important
|
||||
Ongoing development of this recipe is sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
# OpenLDAP
|
||||
|
||||
!!! important
|
||||
Development of this recipe is sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
@@ -40,7 +39,6 @@ mkdir /var/data/openldap/openldap
|
||||
mkdir /var/data/runtime/openldap/
|
||||
```
|
||||
|
||||
!!! note "Why 2 directories?"
|
||||
For rationale, see my [data layout explanation](https://geek-cookbook.funkypenguin.co.nz/reference/data_layout/)
|
||||
|
||||
### Prepare environment
|
||||
@@ -59,7 +57,6 @@ OAUTH2_PROXY_CLIENT_SECRET=
|
||||
OAUTH2_PROXY_COOKIE_SECRET=
|
||||
```
|
||||
|
||||
!!! note
|
||||
I use an [OAuth proxy](https://geek-cookbook.funkypenguin.co.nz/reference/oauth_proxy/) to protect access to the web UI, when the sensitivity of the protected data (i.e. my authentication store) warrants it, or if I don't necessarily trust the security of the webUI.
|
||||
|
||||
Create ```authenticated-emails.txt```, and populate with the email addresses (_matched to GitHub user accounts, in my case_) to which you want grant access, using OAuth2.
|
||||
@@ -334,7 +331,6 @@ Create yours profile (_you chose a default profile in config.cfg above, remember
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this, at (```/var/data/config/openldap/openldap.yml```)
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
```
|
||||
version: '3'
|
||||
@@ -388,7 +384,6 @@ networks:
|
||||
external: true
|
||||
```
|
||||
|
||||
!!! warning
|
||||
**Normally**, we set unique static subnets for every stack you deploy, and put the non-public facing components (like databases) in an dedicated <stack\>_internal network. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
However, you're likely to want to use OpenLdap with KeyCloak, whose JBOSS startup script assumes a single interface, and will crash in a ball of if you try to assign multiple interfaces to the container.
|
||||
@@ -440,7 +435,6 @@ You've now setup your OpenLDAP directory structure, and your administration inte
|
||||
Create your users using the "**New User**" button.
|
||||
|
||||
|
||||
!!! important
|
||||
Development of this recipe is sponsored by [The Common Observatory](https://www.observe.global/). Thanks guys!
|
||||
|
||||
[](https://www.observe.global/)
|
||||
|
||||
@@ -43,7 +43,6 @@ OTR_HOST=owntracks.example.com
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -95,7 +94,6 @@ networks:
|
||||
- subnet: 172.16.15.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -107,7 +107,6 @@ server {
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -192,7 +191,6 @@ networks:
|
||||
- subnet: 172.16.47.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -30,7 +30,6 @@ MYSQL_ROOT_PASSWORD=set-me-and-use-me-when-setting-up-piwik
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
@@ -82,7 +81,6 @@ networks:
|
||||
- subnet: 172.16.4.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -37,7 +37,6 @@ PGID=42
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -81,7 +80,6 @@ networks:
|
||||
- subnet: 172.16.16.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -28,7 +28,6 @@ mkdir /var/data/portainer
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
|
||||
@@ -25,7 +25,6 @@ chmod 777 /var/data/privatebin/
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
|
||||
@@ -14,7 +14,6 @@ Features include:
|
||||
* Drafts saved to local storage.
|
||||
* Handlebars for templates and logic.
|
||||
|
||||
!!! warning "Project likely abandoned"
|
||||
|
||||
In my limited trial, Realms seems _less_ useful than [Gollum](https://geek-cookbook.funkypenguin.co.nz/recipes/gollum/) for my particular use-case (_i.e., you're limited to markdown syntax only_), but other users may enjoy the basic user authentication and registration features, which Gollum lacks.
|
||||
|
||||
@@ -47,7 +46,6 @@ OAUTH2_PROXY_COOKIE_SECRET=
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -95,7 +93,6 @@ networks:
|
||||
- subnet: 172.16.35.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -98,7 +98,6 @@ Create a docker swarm config file in docker-compose syntax (v3), based on the or
|
||||
|
||||
???+ note "This example is 274 lines long. Click here to collapse it for better readability"
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
@@ -378,7 +377,6 @@ Create a docker swarm config file in docker-compose syntax (v3), based on the or
|
||||
- subnet: 172.16.29.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -1,6 +1,5 @@
|
||||
hero: Not all heroes wear capes
|
||||
|
||||
!!! danger "This recipe is a work in progress"
|
||||
This recipe is **incomplete**, and is featured to align the [patrons](https://www.patreon.com/funkypenguin)'s "premix" repository with the cookbook. "_premix_" is a private git repository available to [all Patreon patrons](https://www.patreon.com/funkypenguin), which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
So... There may be errors and inaccuracies. Jump into [Discord](http://chat.funkypenguin.co.nz) if you're encountering issues
|
||||
@@ -48,7 +47,6 @@ MAIL_FROM="Wekan <wekan@wekan.example.com>"
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -101,7 +99,6 @@ networks:
|
||||
- subnet: 172.16.3.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -57,7 +57,6 @@ S6_BEHAVIOUR_IF_STAGE2_FAILS=2
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -114,7 +113,6 @@ networks:
|
||||
- subnet: 172.16.5.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -76,7 +76,6 @@ BACKUP_FREQUENCY=1d
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -174,7 +173,6 @@ networks:
|
||||
- subnet: 172.16.21.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -8,7 +8,6 @@ Wekan allows to create Boards, on which Cards can be moved around between a numb
|
||||
|
||||
There's a [video](https://www.youtube.com/watch?v=N3iMLwCNOro) of the developer showing off the app, as well as a f[unctional demo](https://wekan.indie.host/b/t2YaGmyXgNkppcFBq/wekan-fork-roadmap).
|
||||
|
||||
!!! note
|
||||
For added privacy, this design secures wekan behind an [oauth2 proxy](https://geek-cookbook.funkypenguin.co.nz/reference/oauth_proxy/), so that in order to gain access to the wekan UI at all, oauth2 authentication (_to GitHub, GitLab, Google, etc_) must have already occurred.
|
||||
|
||||
## Ingredients
|
||||
@@ -53,7 +52,6 @@ BACKUP_FREQUENCY=1d
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
```
|
||||
@@ -127,7 +125,6 @@ networks:
|
||||
- subnet: 172.16.3.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
@@ -41,7 +41,6 @@ SSHUSER=batman
|
||||
|
||||
Create a docker swarm config file in docker-compose syntax (v3), something like this:
|
||||
|
||||
!!! tip
|
||||
I share (_with my [patreon patrons](https://www.patreon.com/funkypenguin)_) a private "_premix_" git repository, which includes necessary docker-compose and env files for all published recipes. This means that patrons can launch any recipe with just a ```git pull``` and a ```docker stack deploy```
|
||||
|
||||
|
||||
@@ -85,7 +84,6 @@ networks:
|
||||
- subnet: 172.16.45.0/24
|
||||
```
|
||||
|
||||
!!! note
|
||||
Setup unique static subnets for every stack you deploy. This avoids IP/gateway conflicts which can otherwise occur when you're creating/removing stacks a lot. See [my list](https://geek-cookbook.funkypenguin.co.nz/reference/networks/) here.
|
||||
|
||||
|
||||
|
||||
Reference in New Issue
Block a user